Penetration Testing for Web Applications & Apps

Pentesting for higher cybersecurity
Hacker attacks are especially risky when sensitive information and data are involved. In pentests, we consciously search for security vulnerabilities in IT systems before hackers identify and exploit them.
The goal of pentesting is to identify these gaps at an early stage and thus develop quick solutions.
Be safe with pentesting
The number of cyber attacks has been rising for years. This is why the German Federal Office for Information Security (BSI) also recommends pentestingto check the current security of IT systems. It is important that the tests are scheduled on a regular basis.
This is how we run pentests
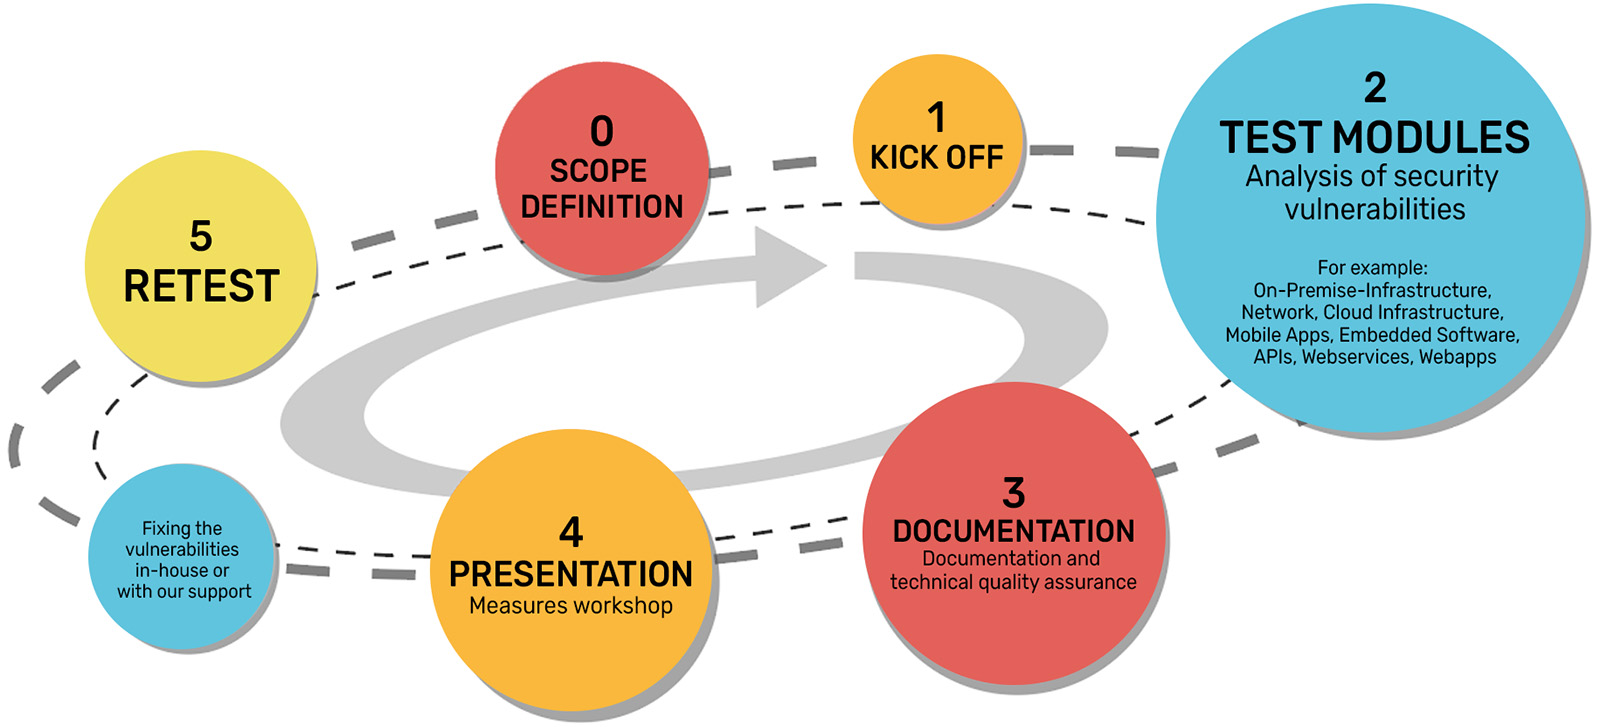
We use a combination of automated tests and manual, explorative procedures. We combine the speed, repeatability and high throughput of automated testing with the creativity, expertise and combinatorial skills of our cybersecurity engineers.
Meanwhile, we draw on well-known databases and repositories such as the U.S. government’s NVD (National Vulnerability Database) or the U.S. Department of Homeland Security’s CVE (Common Vulnerabilities and Exposures) to identify potential vulnerabilities. Drawing on our many years of experience in software engineering— conducted in accordance with the highest IT security standards —we design test and attack scenarios tailored to your software. This allows us to examine potential attack vectors (a single path of attack) or attack surfaces (multi-stage attack methods).
As a result, every vulnerability found is rated using the Common Vulnerability Scoring System (CVSSv3) and tagged with possible mitigation measures, including their effectiveness.
In other words: You get a quick overview of your software’s security status and can use this information to improve it.
We check the corresponding applications (Web/WebApps/Apps) for security risks during our pentests. This sometimes includes front-end and back-end, but also web services, APIs and other components.
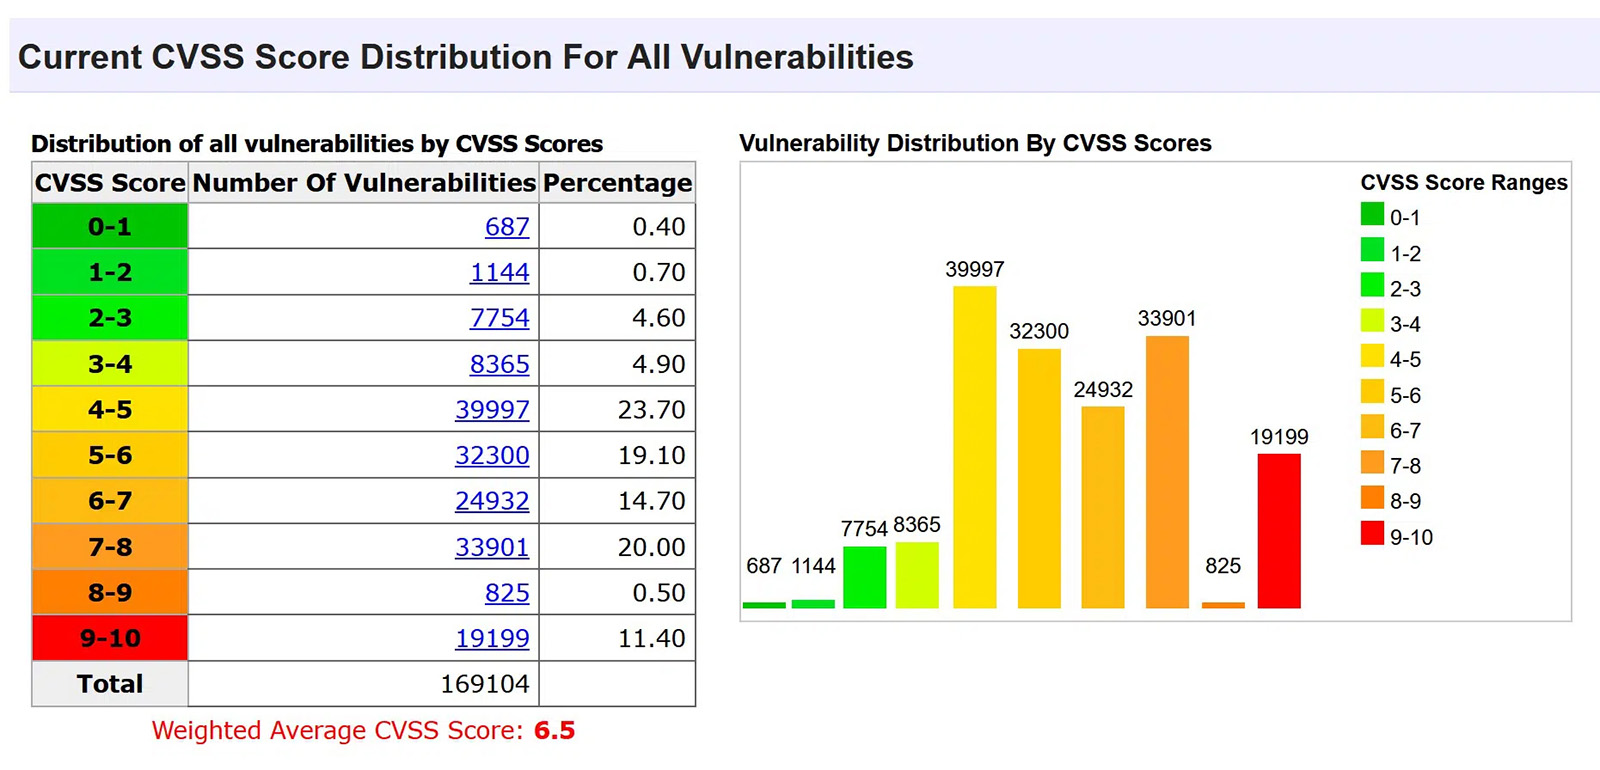
These are the vulnerabilities we test for you
Synergies are our recipe for success
BAYOOTEC and BAYOOMED —many years of experience in software engineering, particularly in safety-critical areas, and IT security combine with expertise in medical software. Through this partnership, we support you with the comprehensive knowledge base of both business divisions. Write us and we will be happy to advise you and talk about the possibilities for more security of your software, medical software, apps and DiGA.
Contact Us Now
Whether you have a specific software project in mind or are looking for answers to questions you have—we’re here to help.
Schedule a no-obligation consultation here.